Next.js APIs and Webhooks Explained: A Practical Guide for Beginners
Software Developer & Digital Tools Creator
Quick Takeaway & Key Insights
Learn how Next.js Route Handlers work, how APIs and webhooks differ, how to handle JSON requests safely, and how to build a simple endpoint without unnecessary complexity.
Modern websites rarely work as isolated pages. A contact form may send data to a server, a dashboard may request account information, or a payment provider may need to notify your application when an event occurs.
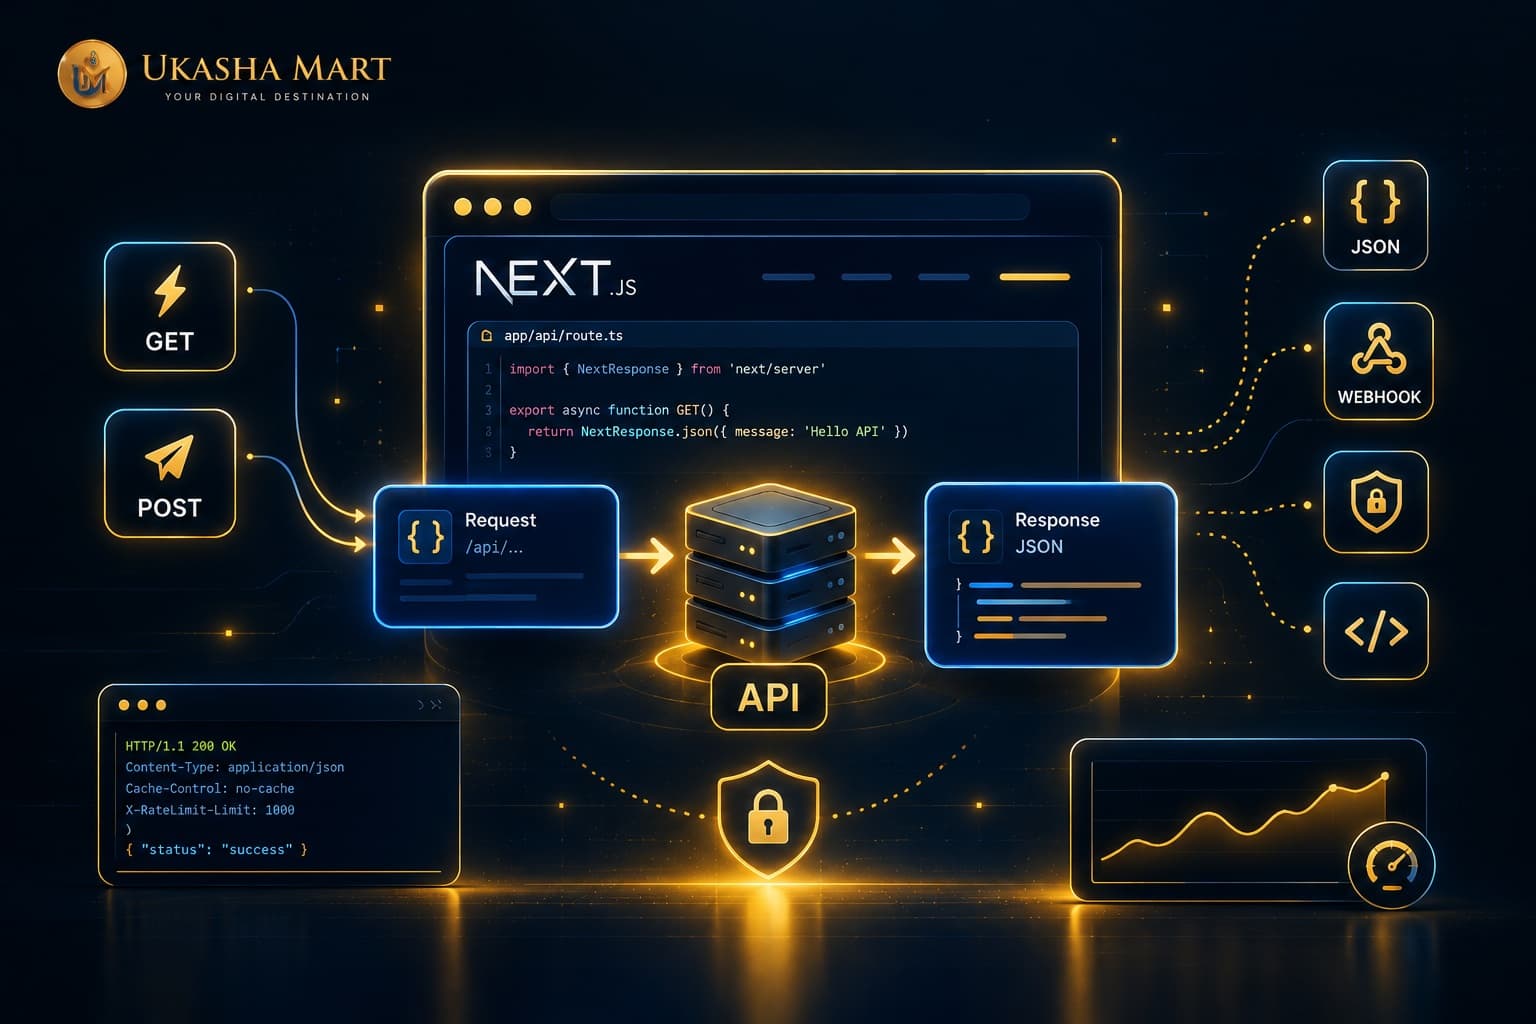
Underneath those features is a simple system: software sends HTTP requests, another system processes them, and a response comes back.
In a Next.js App Router project, Route Handlers provide a practical
way to create custom HTTP request handlers inside the app directory.
They use the Web Request and Response APIs and support methods including
GET, POST, PUT, PATCH, and DELETE. Next.js documents Route
Handlers as the App Router approach for creating custom request
handlers. Next.js Route
Handlers
What Is an API?
An API is a structured way for software to communicate with another piece of software.
Imagine a dashboard that needs a list of projects. The browser could request:
GET /api/projects
The server might return:
{
  "projects": [
    {
      "id": 1,
      "name": "Website redesign"
    }
  ]
}
HTTP methods communicate the intended action. GET is normally used to
retrieve data, while POST commonly submits data and may create a
change on the server. PUT, PATCH, and DELETE are used for other
operations. MDN HTTP
Methods
The important thing is consistency. An endpoint should have a clear purpose and predictable responses.
What Is a Webhook?
A webhook is different because the external service usually starts the communication.
With a normal API request:
Your application → Service
Your application asks for something.
With a webhook:
Service → Your application
The service tells your application that something happened.
For example, a payment provider might send a webhook after a payment succeeds. Your application receives the event and updates an order.
Next.js Route Handlers can receive webhook requests, commonly through a
POST handler. The official documentation demonstrates using a Route
Handler to receive and process webhook payloads. Next.js Route
Handlers
Create Your First Next.js API Endpoint
In the App Router, a Route Handler lives in a route.ts or route.js
file.
For example:
app/
└── api/
    └── hello/
        └── route.ts
The handler can be very small:
export async function GET() {
  return Response.json({
    message: "Hello from the API",
  });
}
The endpoint is now available at:
/api/hello
Next.js supports GET, POST, PUT, PATCH, DELETE, HEAD, and
OPTIONS in Route Handlers. An unsupported method can result in
405 Method Not Allowed. Next.js Route Handler API
Reference
This is useful when a project needs a small server endpoint without immediately creating a separate backend application.
Reading JSON From a POST Request
Suppose a form sends:
{
  "name": "Ukasha",
  "email": "hello@example.com"
}
A Route Handler can read the JSON body:
export async function POST(request: Request) {
  const data = await request.json();

  return Response.json({
    received: data,
  });
}
The browser Request.json() method reads the request body and parses it
as JSON. The returned value is a JavaScript value rather than a JSON
string. MDN
Request.json()
In a real application, do not blindly trust incoming data. Validate required fields and expected formats before storing or forwarding anything.
Why HTTP Status Codes Matter
An API response is not just its JSON body. The status code also communicates what happened.
Common examples include:
200 OK--- the request succeeded.201 Created--- a resource was successfully created.400 Bad Request--- the request cannot be processed as sent.401 Unauthorized--- authentication is required or failed.403 Forbidden--- access is not allowed.404 Not Found--- the requested resource does not exist.405 Method Not Allowed--- the endpoint does not support that method.500 Internal Server Error--- the server encountered an unexpected problem.
HTTP status codes are grouped into informational, successful, redirection, client-error, and server-error classes. MDN HTTP Status Codes
For example:
return Response.json(
  { error: "Email is required" },
  { status: 400 }
);
A predictable status code makes it much easier for the frontend to understand whether it should display a validation message, retry, or show a success state.
Building a Basic Webhook Endpoint
A simple webhook can live here:
app/
└── api/
    └── webhook/
        └── route.ts
A starting implementation could be:
export async function POST(request: Request) {
  try {
    const payload = await request.json();

    // Validate and process the event here.

    return Response.json({ received: true });
  } catch {
    return Response.json(
      { error: "Invalid webhook payload" },
      { status: 400 }
    );
  }
}
This is only the beginning. A production webhook endpoint should verify that the request actually came from the service you expect.
Depending on the provider, verification may involve a signature, secret token, timestamp, or another mechanism.
Webhook Security Is Important
A webhook URL is a public HTTP endpoint. Anyone who discovers it may be able to send requests to it.
Before processing an event, ask:
Can I verify the sender?
Use the provider's recommended signature or authentication mechanism whenever available.
Can the same event arrive twice?
Webhook providers can retry delivery. If processing the same event twice could create a duplicate payment, order, email, or other side effect, use an event ID or transaction ID and design the operation to be safely repeatable.
Are secrets outside the source code?
Avoid:
const secret = "my-super-secret-key";
Use environment variables or the provider's secret-management mechanism instead.
Are public error messages safe?
Do not send database details, API keys, stack traces, or other sensitive information back to an unknown caller. Next.js specifically recommends avoiding sensitive information in errors returned to clients. Next.js Backend for Frontend
Keep Endpoints Focused
A beginner-friendly project can become difficult to maintain when everything is placed inside one giant endpoint.
Instead of:
/api/all
with users, payments, orders, emails, analytics, and webhooks mixed together, use clear boundaries such as:
/api/users
/api/orders
/api/contact
/api/webhooks/payment
The exact structure depends on the application, but each route should have a responsibility that a developer can understand quickly.
Next.js allows Route Handlers to be nested throughout the app
directory, making it possible to organize endpoints around the
application's structure. Next.js Route
Handlers
API vs Webhook: The Easiest Way to Remember
Ask one question:
Who starts the conversation?
If your application starts it:
Your app → Service
you are probably making an API request.
If an external service starts it:
Service → Your app
you are probably receiving a webhook.
A real application can use both at the same time.
For example, an online store might call a shipping API to request delivery information, while the shipping company sends a webhook when the package status changes.
Do You Need a Separate Backend?
Not always.
Next.js supports a Backend-for-Frontend pattern in which Route Handlers can expose public HTTP endpoints and return JSON, XML, files, images, or other content types. Next.js Backend for Frontend
That can be enough for many websites and applications.
It does not mean every application should put its entire backend into Next.js. Larger systems may still need dedicated services, databases, queues, background workers, authentication infrastructure, or other components.
A better rule is:
Use the simplest architecture that comfortably handles the requirements you actually have.
A Practical API and Webhook Checklist
Before deploying an endpoint, check:
- [ ] The route has one clear responsibility.
- [ ] Supported HTTP methods are intentional.
- [ ] Incoming data is validated.
- [ ] Response status codes are meaningful.
- [ ] Secrets are stored outside source code.
- [ ] Authentication is used where necessary.
- [ ] Authorization is checked for protected actions.
- [ ] Duplicate webhook events cannot accidentally create duplicate side effects.
- [ ] Webhook signatures are verified when the provider supports them.
- [ ] Public error messages do not leak sensitive information.
- [ ] Logs are useful without exposing secrets.
- [ ] External-service failures are handled safely.
Test More Than the Happy Path
A successful request in development is only one test.
Try a valid request first.
Then remove a required field. Send malformed JSON. Use the wrong HTTP method. Try an unauthorized request. If the endpoint receives webhooks, send the same event twice and see what happens.
These tests reveal problems that are easy to miss when everything is tested only with perfect input.
A useful API should not merely work when everything goes right. It should also fail in a controlled and understandable way.
How This Fits Into a Next.js Project
A small project might eventually have:
app/
├── page.tsx
├── blog/
│   └── page.tsx
├── tools/
│   └── page.tsx
└── api/
    ├── contact/
    │   └── route.ts
    ├── projects/
    │   └── route.ts
    └── webhooks/
        └── payment/
            └── route.ts
The user interface remains focused on the experience, while Route Handlers provide focused server-side entry points.
The Next.js App Router is file-system based and uses modern React capabilities such as Server Components, Suspense, and Server Functions. Next.js App Router
Final Takeaway
APIs and webhooks sound complicated because they connect several moving parts: browsers, servers, third-party services, databases, authentication, and HTTP.
The core idea is much simpler.
An API gives software a structured way to request or submit information.
A webhook lets a service notify your application when an event occurs.
Next.js Route Handlers provide a practical way to create these HTTP
endpoints directly inside an App Router project. The difficult part is
not writing a POST function. The real engineering work is deciding
what should happen around it: validation, authentication, authorization,
security, duplicate-event handling, useful status codes, and reliable
error handling.
Once those ideas are clear, APIs stop feeling like a mysterious backend feature and become another organized part of building a web application.
Research & References
- Next.js --- Route Handlers: https://nextjs.org/docs/app/getting-started/route-handlers
- Next.js --- Route Handler API Reference: https://nextjs.org/docs/app/api-reference/file-conventions/route
- Next.js --- Backend for Frontend: https://nextjs.org/docs/app/guides/backend-for-frontend
- Next.js --- App Router: https://nextjs.org/docs/app
- MDN --- HTTP Request Methods: https://developer.mozilla.org/en-US/docs/Web/HTTP/Reference/Methods
- MDN --- HTTP Response Status Codes: https://developer.mozilla.org/en-US/docs/Web/HTTP/Reference/Status
- MDN --- Request.json(): https://developer.mozilla.org/en-US/docs/Web/API/Request/json
- Google Search Central --- Creating Helpful, Reliable, People-First Content: https://developers.google.com/search/docs/fundamentals/creating-helpful-content
Try our QR Code Generator
Create clean, scannable QR codes for testing websites, URLs, and client handoffs.
Ukasha Altaf
Software Developer & Digital Tools Creator
Founder of Ukasha Mart. Building free, accessible browser-based utilities and writing in-depth tutorials on modern technology, freelancing, and practical online work.
Explore Further